What Happens When It Stops Working? – Predrag Puharić on digital dependency, public services and the choices cities need to retain
by Svetlana Tesic, CoFounder Mayors of Europe
Digitalization creates fragility. The question is how much fragility our cities can absorb.
ENISA’s Threat Landscape 2025, analyzing 4,875 incidents recorded across the EU between July 2024. and June 2025, found that public administration accounted for 38.2% of incidents attributed to a specific sector, making it the most targeted sector in the dataset. As cities become increasingly reliant on digital systems to deliver essential services, resilience is no longer only a matter of cybersecurity. It is also about governance, procurement, accountability, data, suppliers and the ability to keep essential services running when disruption comes.
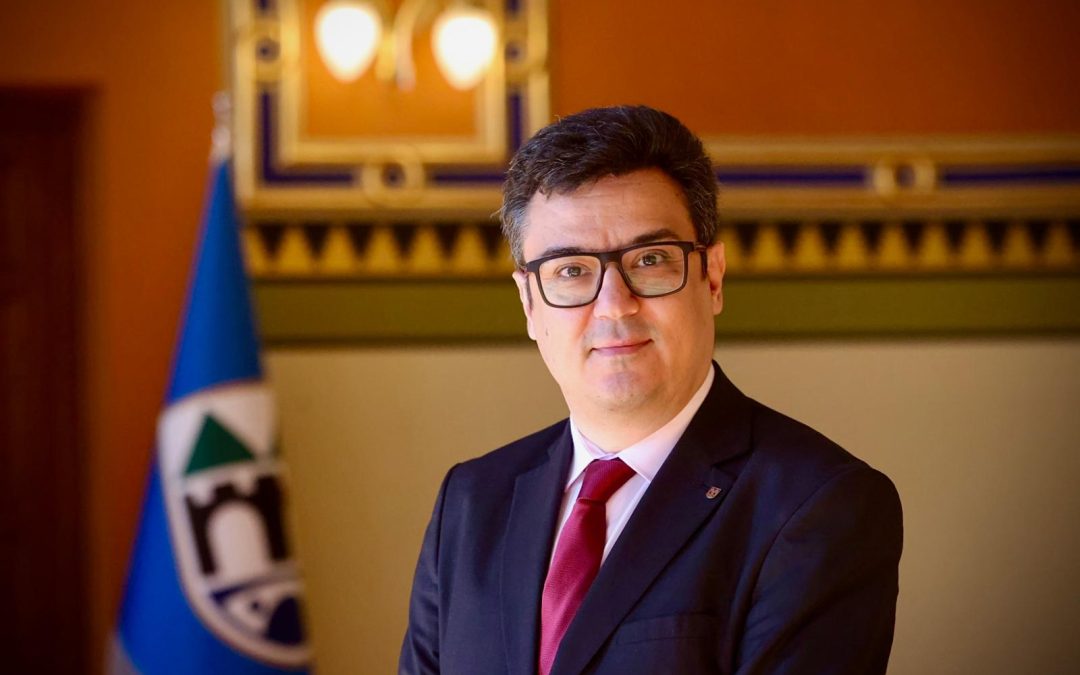
Predrag Puharić, Deputy Mayor of Sarajevo and a cybersecurity policy and governance expert, brings both perspectives to the table. Having worked across city administration and cybersecurity, he offers a practical view of what cities need to understand, question and change as their digital dependencies grow.
Your experience spans city administration and cybersecurity. What do these two worlds often misunderstand about each other? What has your experience taught you about bringing them together?
Cybersecurity professionals sometimes look at a city as if it were simply a large organisation with an IT department. It is much more complicated than that. A city is an ecosystem of public authorities, utilities, service providers, transport systems, cultural institutions, private contractors and, most importantly, people who depend on those services every day.
On the other hand, city administrations can still see cybersecurity as a technical issue, something for the IT department to solve. That is equally problematic. If a digital service becomes unavailable, if a transport system is disrupted or if sensitive citizen data is compromised, this is no longer an IT problem. It becomes a governance problem and, very quickly, a public-service problem.
My experience in both fields has taught me that we need a common language centred on risk, public value and continuity of services.
Cybersecurity professionals need to understand how cities actually govern, including fragmented responsibilities, procurement rules, limited resources and different levels of government. Political and administrative leaders, meanwhile, need to understand that digital risk cannot simply be delegated.
And there is another important point: responsibility for urban services is not always located at City Hall. In Sarajevo, as in many European cities, competencies are divided between the City, the Canton, municipalities, public companies and other institutions. Resilience therefore depends as much on coordination as it does on technology.
Ultimately, the question city leaders should be asking is not simply, “Are our systems secure?” It is: Can we continue serving people when something goes wrong?
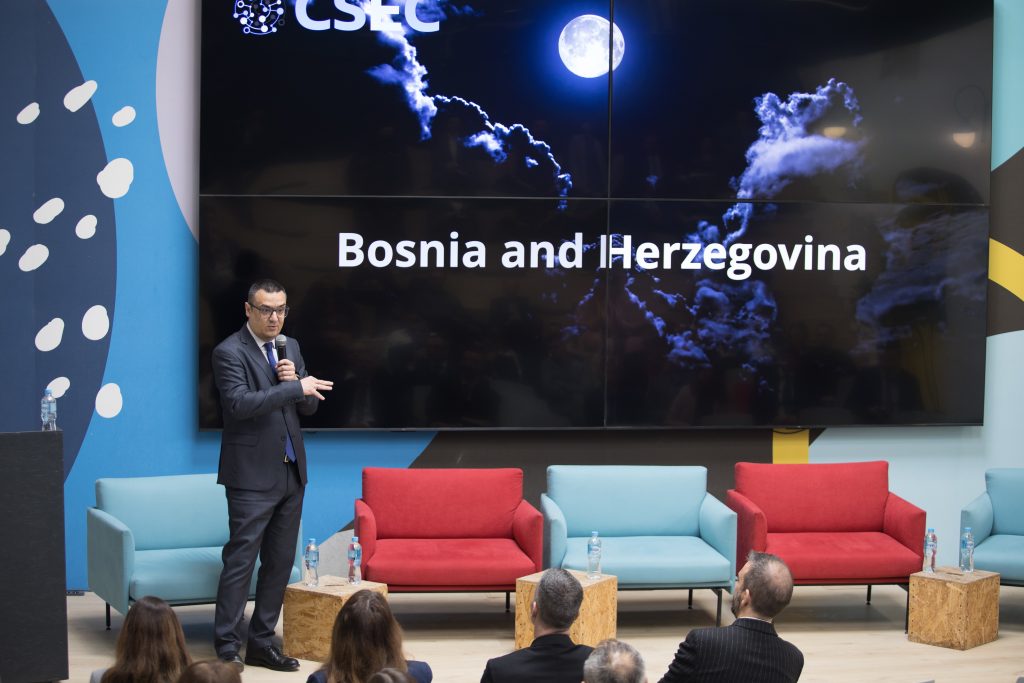
photo credit: Predrag Puharic
We have spent years talking about building “smart cities”. Do you think cities now need to shift their focus from being smarter to being more resilient? What does that change in practice?
I do, although I would not put “smart” and “resilient” in opposition to each other. We should change what we mean by a successful smart city.
For years, the smart-city conversation was dominated by connectivity: more sensors, more data, more platforms, more automation. These technologies can create enormous public value, but every new connection also creates a dependency.
A traffic-management platform may make mobility more efficient, but what happens when it is unavailable? A cloud service may significantly improve public administration, but can the city retrieve its data and move to another provider? An AI system may improve decision-making, but do we understand how its decisions are made, which data it uses and who remains accountable?
Resilience means asking those questions before deployment, not after an incident.
For me, a smart city should therefore also be secure by design, interoperable, recoverable and capable of operating under degraded conditions. It should know which services are critical, where its dependencies are and how quickly they can be restored.
This also changes procurement. The cheapest or most feature-rich solution is not necessarily the solution that creates the greatest long-term public value. Cities need to consider cybersecurity, interoperability, data portability, lifecycle support and exit strategies from the beginning.
The real evolution is therefore from technology-centred smart cities towards citizen-centred resilient cities.
Technology remains important. But the measure of success is no longer how much technology a city deploys. It is whether that technology makes the city more capable, more trustworthy and better able to serve its residents.
If you were advising the leadership of a city that knows it needs to improve its digital resilience but doesn’t know where to start, what would you tell them to do first?
I would actually tell them not to start by buying technology.
Start by understanding what you need to protect and what absolutely needs to continue functioning.
The first step is governance: someone at leadership level must own digital resilience, and responsibilities must be clear. Cybersecurity cannot exist somewhere between the IT department, procurement, legal affairs and external suppliers with nobody ultimately accountable.
Then identify your critical services and dependencies. What would have the greatest impact on residents if it stopped working for an hour, a day or a week? Which systems, suppliers, networks and datasets support those services?
From there, I would concentrate on a small number of fundamentals: knowing your assets, managing vulnerabilities and access, maintaining tested backups, preparing an incident-response and recovery plan, and ensuring that critical suppliers meet appropriate security requirements.
And then I would test it.
A tabletop exercise involving political leadership, administration, IT teams, communications, utilities and relevant external partners can reveal more about a city’s actual readiness than another strategy document.
For cities with limited budgets, this prioritisation is particularly important. Resilience does not necessarily begin with a sophisticated security operations centre or an expensive new platform. Many significant improvements come from governance, basic cyber hygiene, tested recovery procedures and better procurement.
I would also encourage cities not to work in isolation. Municipalities often face very similar threats but have very different capacities. Shared expertise, common standards, regional cooperation and shared cybersecurity services can be far more realistic than expecting every city to build the same capabilities independently.
As cities increasingly depend on AI, cloud services, connected infrastructure and external technology providers, how can they innovate while retaining meaningful control over their data and digital infrastructure?
I think we need to be careful with the term digital sovereignty. For a city, sovereignty does not mean building every piece of technology itself, operating its own cloud or refusing to work with global technology companies.
That would often be inefficient and, in some cases, less secure.
Digital sovereignty means retaining meaningful control and meaningful choice.
A city should know where its important data is, who can access it, how it is protected and under which jurisdiction it is processed. It should be able to retrieve that data in a usable format. Systems should use interoperable standards wherever possible, and there should be a credible way to change suppliers without having to rebuild an entire digital ecosystem.
That makes procurement extremely important.
Before adopting a cloud platform, AI service or connected urban system, cities should be asking questions about data ownership, portability, security responsibilities, audit rights, subcontractors, incident notification, software lifecycle and the conditions under which the relationship can be terminated.
Vendor lock-in is not simply a commercial issue. When a public authority becomes technically unable or financially unable to change provider, it can become a governance issue.
AI adds another dimension. Public authorities should understand what a system is being used for, what data feeds it, where human responsibility remains and whether its use can meaningfully be explained to citizens.
None of this should prevent innovation. In fact, good governance makes sustainable innovation possible.
The objective is not technological independence. It is strategic autonomy: the ability of a public institution to make choices rather than have those choices made for it by technological dependency.
Digitalization only works if citizens trust it. Where should cities draw the line between collecting useful urban data and creating systems that feel intrusive or like surveillance?
I think the starting point is very simple: just because we can collect data does not mean we should.
Cities legitimately need data. We cannot improve mobility, air quality, energy efficiency or public services without understanding how the city works. But every collection of data should begin with a clearly defined public purpose.
Then we need to ask whether the data is actually necessary and proportionate to that purpose.
There is an important distinction between knowing that 5,000 vehicles passed through an intersection and knowing who was driving each of them. Technology may allow us to collect both. Public interest may require only the first.
That principle becomes even more important as sensors, cameras, artificial intelligence and different datasets are combined.
Privacy therefore cannot be something we assess immediately before launching a system. It should be part of its architecture from the beginning: data minimisation, defined retention periods, appropriate access controls, security safeguards and, where processing creates significant risks for individuals, proper data-protection impact assessments.
Transparency is equally important. Citizens should be able to understand what information their city collects, why it is collected, how long it is retained and who can use it.
And finally, we need democratic limits. Some technologies may be technically effective but still be inappropriate for a democratic public space.
Trust is not something a city can create afterwards through communication.
Trust has to be designed into the system.
Looking to the future, what would a genuinely resilient city look like, and what do cities need to start doing differently today to get there?
A resilient city is not a city where nothing ever goes wrong. Such a city does not exist.
It is a city that understands its vulnerabilities, prepares for disruption, continues delivering its most important services and recovers quickly when an incident occurs.
By 2030, I would expect resilient cities to understand their critical digital dependencies just as seriously as they understand physical infrastructure. Cybersecurity, data governance and continuity planning should be embedded in decisions about mobility, energy, public services, utilities and urban development rather than treated as separate technology programmes.
Procurement will also need to change. Cities should increasingly purchase not only functionality, but resilience: security by design, interoperability, recoverability, portability and long-term maintainability.
I also think collaboration will become essential. Thousands of European municipalities cannot each develop every specialised cybersecurity capability independently. We need stronger mechanisms for sharing expertise, threat information, standards, infrastructure and response capacity between cities and across levels of government.
But technology is only part of resilience.
A genuinely resilient city also needs institutions that citizens trust, public servants who understand digital risk, clear accountability and services designed around people’s actual needs.
That is particularly important because our cities will simultaneously face technological disruption, climate risks, demographic change and growing pressure on public finances.
So the change I would like to see is fundamentally one of mindset.
For too long, digitalisation has often been measured by what we deploy.
I think the next generation of European cities should measure it by what public value we create, how much control we retain, how well we protect people’s rights, and how effectively we can continue serving them when circumstances become difficult.
That, for me, is the difference between a city that is merely smart and one that is genuinely resilient.
Predrag Puharić
Cybersecurity Policy & Governance Expert, Public Sector Digital Resilience, Deputy Mayor of Sarajevo, CEO, CSEC
www.csec.ba predragpuharic.info
Source: ENISA, Threat Landscape 2025, analysis of 4,875 incidents recorded from 1 July 2024 to 30 June 2025.